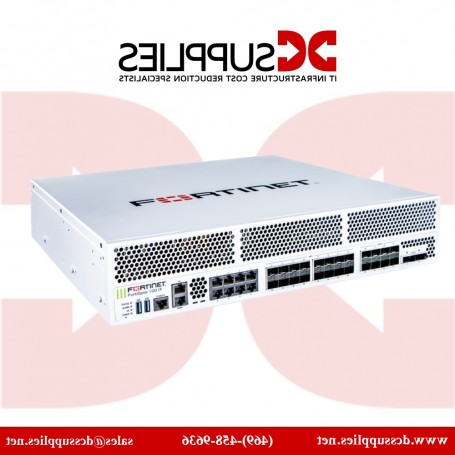
Fortinet FSM-500G
FortiSIEM 500G Collector Security Appliance – High-Performance Log Collection & Threat Analytics
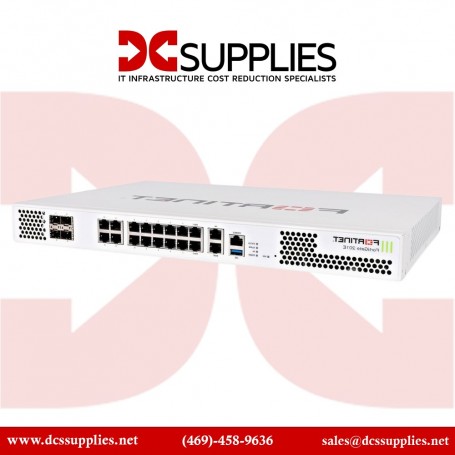
The Fortinet FSM‑500G FortiSIEM Collector is a robust security information and event management (SIEM) appliance built for centralized log collection, correlation, and real‑time analytics. Designed for medium to large enterprises, it delivers comprehensive visibility across your infrastructure to detect threats and maintain compliance.
Features :
Engineered for high‑throughput log ingestion, the FSM‑500G processes and correlates events from both Fortinet devices and third‑party sources. Its scalable architecture supports growing data volumes, allowing security teams to rapidly identify anomalies, suspicious behavior, and policy violations.
Advanced Options :
Integrating seamlessly with the Fortinet Security Fabric, this appliance enhances coordinated defense and accelerates incident response. Comprehensive reporting and auditing capabilities simplify regulatory compliance, while the intuitive management interface streamlines daily security operations.
Product Key Features
- High‑throughput log collection and event correlation
- Real‑time threat analytics and anomaly detection
- Integration with Fortinet Security Fabric and third‑party devices
- Compliance reporting and auditing capabilities
- Scalable design for medium to large enterprise deployments
Reliability & Performance :
Built for continuous operation, the FSM‑500G pairs powerful hardware with optimized FortiSIEM software for reliable, high‑availability performance. Redundant power options and enterprise‑grade components ensure uptime, while FortiCare services keep the system updated with the latest features and security patches.
Key Features :

Write a Review